Application Allowlisting: Why It Stops Ransomware That Antivirus Misses
An office manager at a 50-person company gets a call from someone claiming to be from the bank's fraud team. The caller walks her through downloading a "secure support tool." Antivirus doesn't object, because the tool is a legitimate remote access program used by thousands of real IT teams. By the next morning, an attacker has used that same tool to reach the file server.
Nothing in that chain looked like malware, so a tool built to recognize malware had nothing to catch. Application allowlisting works from the opposite direction. Instead of trying to spot every bad program, it lets only approved programs run and blocks everything else by default. This post covers why that difference matters for ransomware, what allowlisting does and doesn't do, how a company with 25 to 200 employees rolls it out without disrupting work, and how it fits with the antivirus and EDR you may already have.
How ransomware gets past antivirus
Traditional antivirus compares files against a list of known threats and suspicious behavior. That still catches a lot. It struggles with three patterns that show up again and again in ransomware attacks.
New or modified malware. The FBI's 2024 Internet Crime Report logged 3,156 ransomware complaints and identified 67 new ransomware variants in that year alone. A variant nobody has seen yet has no signature to match.
Legitimate tools used for bad purposes. Attackers increasingly use software that is not malware at all. A joint advisory from CISA, NSA and MS-ISAC, AA23-025A, described attackers sending victims portable versions of real remote monitoring and management tools. Portable versions run without installation and without administrator rights. Antivirus has no reason to flag a signed, widely used remote support program.
Turning off the defenses first. Ransomware operators now routinely try to disable security software before they encrypt anything. In August 2025, Singapore's Cyber Security Agency issued an advisory on an "EDR killer" tool used by multiple ransomware groups, which abuses vulnerable drivers to shut down endpoint protection. Once the alarm is off, everything that follows is quiet.
All three share one weakness from the attacker's side: each step needs a program to run on your computer that you never approved. That is the gap allowlisting closes.
What application allowlisting actually does
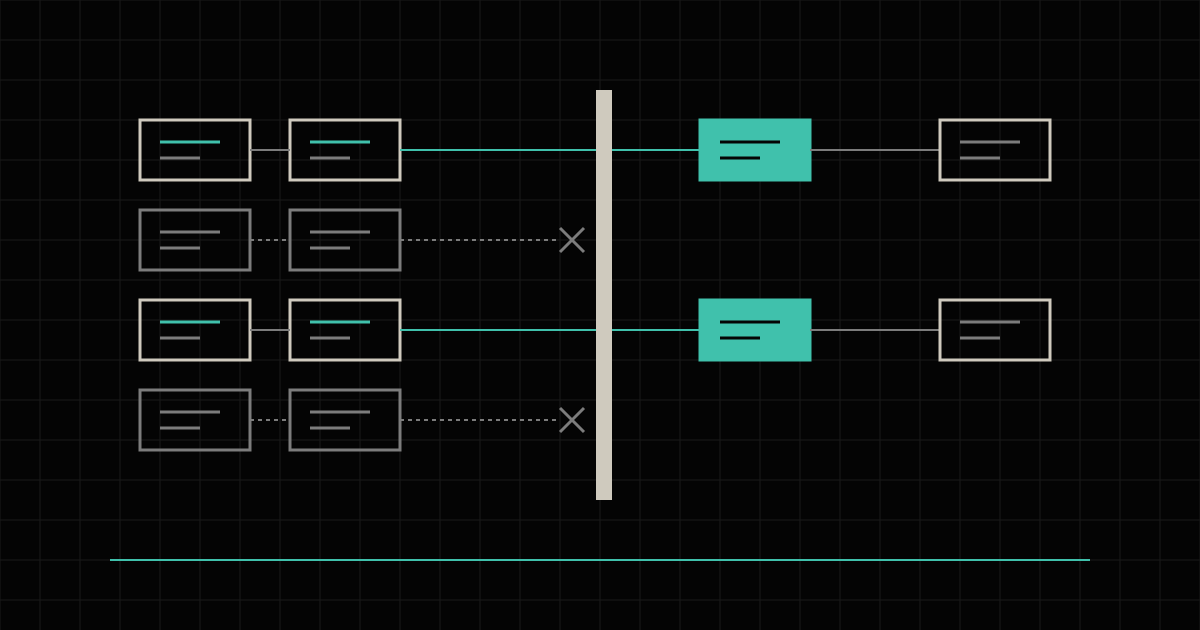
Application allowlisting (also called application control, and in older material "whitelisting") flips the default. A computer runs only the software on an approved list. Anything else, whether it's ransomware, a portable remote access tool, or a game someone downloaded, is blocked before it starts.
NIST describes the approach in SP 800-167, its Guide to Application Whitelisting. The approved list can be defined by several attributes:
- Publisher or digital signature: allow anything signed by a trusted vendor, so routine updates keep working
- File hash: allow one exact version of one file
- File path: allow programs that live in protected folders where standard users can't write
- File name and size: weaker on their own, since both are easy to fake
NIST recommends combining attributes rather than relying on a single one. In practice, most rules for a growing company are publisher-based, with a short list of hash or path rules for in-house or niche software.
Government guidance puts this control near the top of the list. CISA's #StopRansomware Guide, co-authored with the FBI and NSA, recommends application allowlisting and endpoint detection as defenses against the malware that typically precedes ransomware. Australia's Signals Directorate includes application control in its Essential Eight, and its most basic maturity level requires it on workstations, including the user profile and temporary folders where downloaded files usually land.
Antivirus, EDR and allowlisting side by side
These tools answer different questions, which is why mature setups use more than one.
| Control | Question it answers | Main blind spot |
|---|---|---|
| Traditional antivirus | Does this file look like known malware? | New variants and legitimate tools |
| EDR | Is this activity behaving like an attack? | Needs someone watching alerts |
| Application allowlisting | Is this program approved to run at all? | Abuse of tools already approved |
The last row matters. Allowlisting doesn't stop an attacker who abuses software you already allow, such as PowerShell used by an administrator account. That's why it works best alongside EDR and monitoring, not as a replacement. Our earlier comparison of EDR and traditional antivirus covers the detection side in more detail.
What it costs when ransomware gets through
Ransomware is not a large-company problem that occasionally reaches smaller ones. Verizon's 2025 Data Breach Investigations Report found ransomware in 44% of the breaches it reviewed, up from 32% the year before. Among small and mid-sized businesses, ransomware was present in 88% of breaches, compared with 39% at large organizations.
The same report put the median ransom paid at $115,000, and 64% of victims did not pay at all. The ransom is only part of the bill. IBM's Cost of a Data Breach Report 2025 put the average cost of a ransomware or extortion incident at $5.08 million when the attacker disclosed it, and the average U.S. breach across all types at $10.22 million. Those averages skew toward larger organizations, but the cost categories are the same at 50 employees: days of downtime, outside forensics, legal counsel, notification letters, and staff time spent rebuilding instead of working.
For a company that bills $15 million a year, a single week of shutdown is roughly 2% of annual revenue before any recovery spending. Allowlisting won't remove every risk, but it removes the most common way an attacker turns a phishing click into running code.
How a growing company rolls it out
Allowlisting has a reputation for breaking things and generating complaints. Most of that comes from turning it on all at once. A staged rollout avoids it.
- Inventory first. Deploy the control in audit mode, where it logs what would be blocked but blocks nothing. Run it for two to four weeks to capture month-end, payroll and other periodic software.
- Build rules from what you find. Approve trusted publishers (your operating system, office suite, browser, line-of-business vendors). Add specific rules for the handful of tools that aren't signed.
- Remove what shouldn't be there. The audit log usually surfaces unapproved remote access tools, old utilities and personal software. Decide what stays, and remove the rest before enforcement.
- Enforce in rings. Start with a pilot group, then one department at a time. Keep the user profile and download folders locked down, since that's where malicious files usually try to run.
- Set up a fast approval path. Staff need a simple way to request new software, and someone has to answer the same day. A slow process is how allowlisting gets switched off.
- Review on a schedule. Remove rules for software you no longer use, and watch blocked-execution logs for signs of an attack in progress.
On Windows, this is built in through AppLocker and App Control for Business. Dedicated allowlisting products add easier rule management and request workflows. The technology is the smaller part of the job. Keeping the list accurate as the company changes is the work that decides whether allowlisting stays on.
Example engagement: a 70-person engineering firm runs an audit-mode pass and finds three different remote access tools installed by past vendors, plus a file-sharing app nobody approved. Elevaire would confirm with the firm's IT provider which remote tool it actually uses, remove the other two, move file sharing to the approved platform, and then enforce allowlisting one office at a time with a same-day request process for new software.
Where managed security fits
Allowlisting is a "set it up and then keep it right" control. The setup takes weeks. The upkeep never stops: new hires need software, vendors change their signing certificates, and every blocked execution is a small question someone has to answer.
That ongoing ownership is what Elevaire Managed Security provides. Ransomware and application allowlisting are part of every package, along with email security, device management, and multi-factor sign-in. Elevaire handles the rules, the approval requests, and the review of blocked attempts, and the Plus and Complete packages add 24/7 detection and response for the moments when something suspicious does try to run. A full list of what's covered is in what Elevaire Managed Security includes.
Elevaire works alongside your existing IT provider or internal team. They keep running the help desk, the network and the laptops. Elevaire runs the security layer, including the allowlist, and coordinates with them when a rule change touches their tools.
Frequently Asked Questions
How much does application allowlisting cost for a small business?
The software can be inexpensive or already included, since Windows ships with AppLocker and App Control for Business. The real cost is the staff time to build rules, approve requests and review logs every week. Elevaire includes allowlisting in its managed security packages at predictable monthly pricing with no hourly billing, so the upkeep isn't a separate project you have to budget for.
Does application allowlisting replace antivirus or EDR?
No. Allowlisting decides what is allowed to run, while antivirus and EDR watch what approved programs actually do. Attackers who abuse tools you already allow, or who steal an administrator account, can still cause damage without new software. CISA's ransomware guidance recommends using these controls together.
Will allowlisting slow down our employees?
It shouldn't if the rollout starts in audit mode and builds rules from real usage. Most daily work uses a stable set of applications that get approved up front. The friction point is new software requests, which is why a fast, simple approval process matters more than the technology itself.
How does this work alongside our existing IT provider?
Your IT provider keeps doing what it does today: support, devices, network and user setup. Elevaire manages the security controls, including the allowlist, and coordinates with your provider so their remote support and management tools stay approved. Elevaire does not replace your MSP or internal IT team.
How do we get started with application allowlisting?
Start by finding out what software is actually running across your computers, since most companies are surprised by the list. An audit-mode deployment does that without blocking anything. Our security baseline checklist for growing companies shows where allowlisting fits among the other controls worth having in place.
About Elevaire Systems
Elevaire Systems is a managed security services provider for growing companies. We run your security tools and vendors, watch for threats and stop attacks for one predictable monthly price, with virtual CISO leadership and compliance readiness when you need more.
See Where Your Security Stands
Take the free 3-minute scorecard for your top security risks, or book a 30-minute Risk Snapshot to talk it through.