AI Meeting Note Takers: The Security Questions Nobody Asks
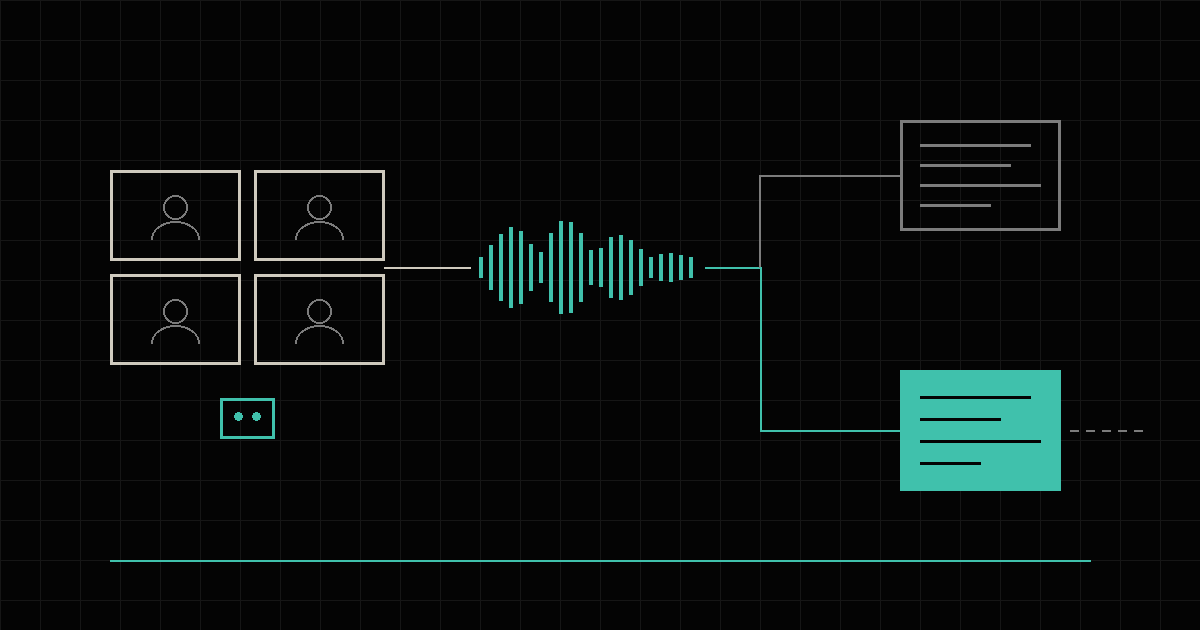
A sales director at a 90-person company connects a free AI note taker to her calendar so she never has to type up call notes again. From then on, a bot joins every meeting on her calendar: client pricing calls, a vendor negotiation, and a performance conversation with a member of her team. Each transcript goes to a vendor's cloud, and a summary lands in the inbox of everyone who was invited.
Nobody approved the tool, and nobody asked the people on the other end of those calls. This post covers how note takers get into meetings, what happens to the recordings, what recent lawsuits say about consent, and the controls that let your team keep the tool without the exposure.
How note takers get into your meetings
AI note takers arrive in three common ways.
- Built into the meeting platform. Zoom AI Companion and Microsoft Teams with Copilot can transcribe and summarize meetings. These features sit inside a platform your company already pays for and controls through an admin console.
- A bot that joins the call. Tools like Otter.ai and Fireflies.ai connect to a user's calendar and send a bot into meetings as a separate participant. Many can join every meeting automatically, including ones the user doesn't host.
- A desktop app with no visible bot. Some newer tools capture audio directly from the user's computer. Nothing appears in the participant list, so other attendees may not know a transcript exists.
The second and third types are usually adopted by individual employees with a work email and a few clicks, the same pattern as other shadow AI.
How common this is
In a July 2026 survey of 500 employed U.S. adults, run by the law firm Kolmogorov Law and reported by Stacker, 33.4% said an AI note taker or transcription bot had been present in their work meetings. About 65% of those workers said they were not consistently asked for consent first.
Coverage of IBM's 2026 Cost of a Data Breach Report by Cybersecurity Dive found that more than two-thirds of organizations said they had no governance process in place to limit shadow AI. The same report put the global average cost of a data breach at a record $4.99 million.
The security questions nobody asks
Someone in the company should be able to answer these before a note taker joins another meeting.
Did everyone on the call agree to be recorded?
Most states require only one participant's consent to record. A group of states requires every participant's consent, including California, Florida, Illinois, Maryland, Massachusetts, Montana, New Hampshire, Pennsylvania and Washington, according to a January 2026 Bloomberg Law analysis. Your company might be in a one-party state while a client on the call is in California.
Vendor terms typically put this on the user. When Otter.ai was sued in 2025, the company said its terms make users responsible for obtaining any necessary permissions before recording.
Where does the recording go, and can the vendor train on it?
Read the vendor's terms for three things: where the audio and transcripts are stored, whether the vendor uses them to train its AI models, and whether that training can be turned off.
Answers differ widely. Zoom states that it does not use customer audio, video, chat or other communications content to train its own or third-party AI models. Microsoft states that prompts, responses and data accessed through Microsoft Graph aren't used to train the foundation models behind Microsoft 365 Copilot. Some standalone note takers describe training on "de-identified" recordings, and that practice is at the center of the lawsuits covered below.
Who receives the summary?
Many note takers email a summary to every invitee after the meeting. In a 2024 incident reported by Fortune, a researcher received an automated transcript after a call with a venture capital firm. The transcript included the investors' private discussion after he had left the call, and he walked away from the deal.
Check where summaries go by default, whether external attendees receive them, and whether the recording keeps running after the host leaves.
How long is it kept, and who can search it?
A year of recorded meetings becomes a searchable archive of everything said about clients, staff and pricing. It can be requested in litigation, exposed in a vendor breach, or read by anyone who gets into the account. Ask what the default retention period is and whether an admin can shorten it. Zoom, for example, offers a zero-retention option for the transcripts behind its AI meeting summaries.
What happens when the employee leaves?
When an employee signs up for a note taker with a work email, the transcripts usually sit in an account that employee controls. After they leave, the company may have no way to retrieve or delete them.
What the lawsuits say about consent
Several class actions now test whether AI note takers break wiretapping and privacy laws. None has reached a final judgment.
- Otter.ai. The consolidated case, In re Otter.ai Privacy Litigation, was filed in the Northern District of California in 2025 by people recorded in meetings who never had Otter accounts. On August 13, 2026, the judge dismissed some claims but let the core wiretap and Illinois biometric privacy claims proceed. A key factor was the allegation that Otter trains its models on recordings, which made it plausible the company acted as a third-party eavesdropper rather than a tool of the host.
- Granola. A proposed class action filed July 30, 2026, alleges that Granola's desktop note taker recorded participants who never knew it was there, and used recordings for AI training by default. A Barnes & Thornburg alert notes these are allegations only and Granola had not yet responded on the merits.
The suits name the vendors, but the Bloomberg Law analysis above flags that a company deploying a tool may face its own exposure when participants weren't told. This isn't legal advice; ask your attorney how your states' consent rules apply.
A practical policy for meeting note takers
A short rule set works better than a ban, since staff who find these tools useful will keep using them. Some meetings, like those with legal counsel, shouldn't produce a transcript at all, because a recording can undermine privilege.
| Meeting type | Note taker allowed? | Condition |
|---|---|---|
| Internal team meetings | Yes | Approved tool only |
| Client and vendor calls | Yes, with notice | Announce it and offer to turn it off |
| Legal, HR and disciplinary | No | Take manual notes |
| Board executive sessions | No | Minutes taken by the secretary |
| Interviews and candidate calls | Only with consent | Ask the candidate at the start |
Put the rules in writing alongside the rest of your AI acceptable use policy so staff know which tools are approved and which data stays out of AI tools entirely.
Technical controls that back up the policy
These controls are available in most Microsoft 365, Google Workspace, Zoom and Teams environments.
- Restrict third-party app consent. Require admin approval before employees can connect new apps to their work calendar or email.
- Review existing connections. Pull the list of apps already connected to company accounts and look for note takers nobody approved. Revoke the ones you don't want.
- Pick one approved tool and configure it. Turn off auto-join for external meetings, turn off automatic summary emails to external attendees, and set a retention period that matches how long you actually need transcripts.
- Use the meeting platform's controls. Waiting rooms and lobby settings let a host see and remove unknown bots.
- Add note takers to offboarding. When someone leaves, revoke their app connections and confirm transcripts sit in a company-owned account, not a personal one.
- Vet the vendor before approving it. Confirm where data is stored, whether it trains models on your content, whether training can be disabled, and what happens to data when the contract ends.
How Elevaire handles this alongside your IT provider
Elevaire Managed Security covers the technical side of this problem. That includes locking down app consent, reviewing which third-party apps can reach email and calendars, enforcing multi-factor sign-in, and managing the security vendors you approve. The quarterly security review is where new connections get checked.
A virtual CISO handles the decisions: writing the meeting recording rules, running longer vendor assessments for AI tools that will touch client data, and reporting AI risk to leadership. Elevaire works alongside your existing IT provider or internal team; it doesn't replace them.
Example engagement: a 50-person accounting firm finds that eight employees have connected four different AI note takers to their work calendars, and two of those tools record client calls by default. Elevaire would inventory the connected apps, review each vendor's data terms, help leadership pick one approved tool with training and external sharing turned off, revoke the rest, and add a short meeting recording section to the firm's acceptable use policy.
Frequently Asked Questions
Is it legal to use an AI note taker in meetings?
Generally yes, if you follow recording consent laws. Several states, including California, Florida, Illinois and Pennsylvania, require consent from everyone on the call. The safest practice is to announce the note taker at the start of every meeting with external participants and offer to turn it off. Ask your attorney how the rules apply to your locations and clients.
Do AI note takers use our meetings to train their AI models?
It depends on the vendor and the plan. Zoom and Microsoft state that they don't use meeting content from their business products to train foundation models. Some standalone tools use de-identified recordings for training by default, which is a central issue in current lawsuits. Confirm in the vendor's terms whether training can be turned off at the admin level.
How much does it cost to manage AI tool risk at a small company?
Most of the work is configuration and policy, using settings you already own, not new software. Elevaire Managed Security covers app consent controls, vendor management and quarterly reviews with predictable monthly pricing and no hourly billing. For context on the downside, IBM's 2026 research put the global average cost of a data breach at $4.99 million.
How does this work alongside our existing IT provider?
Elevaire works with your current IT provider or internal team, not instead of them. Your IT provider keeps handling devices, users and support. Elevaire sets the security controls, such as app consent restrictions and vendor reviews, and coordinates changes with your IT team.
How do I get started with controlling AI note takers?
Start by pulling the list of third-party apps connected to company email and calendar accounts. That one report usually shows how many note takers are already in use. Then pick one approved tool, configure its sharing and retention settings, and write a short rule for which meetings can be recorded.
About Elevaire Systems
Elevaire Systems is a managed security services provider for growing companies. We run your security tools and vendors, watch for threats and stop attacks for one predictable monthly price, with virtual CISO leadership and compliance readiness when you need more.
See Where Your Security Stands
Take the free 3-minute scorecard for your top security risks, or book a 30-minute Risk Snapshot to talk it through.