Sharing Controlled Unclassified Information With Subcontractors Safely
A program manager at an 80-person machine shop needs a quote from the plating vendor down the road by Friday. The fastest way to get it is to attach the full drawing package from the prime to an email and hit send. That drawing package is marked CUI, the plating vendor uses a free email account, and nobody at either company will think about it again unless something goes wrong.
That moment, repeated a few times a week, is where much of the real risk around controlled unclassified information (CUI) sits for small and mid-sized defense suppliers. This post covers what the rules require when you pass CUI to a subcontractor, where sharing usually goes wrong, and a process a 25 to 200 employee contractor can run without slowing production.
Why subcontractor sharing is where CUI leaks
Defense manufacturing is layered. A prime hands a drawing package to a tier-one supplier, who sends pieces of it to a machinist, a heat treater, a coating shop and an inspection lab. Each handoff is a copy that lands on someone else's systems, under their controls rather than yours.
Three patterns show up again and again:
- The whole package goes when one page would do. A finishing vendor needs the part geometry and the finish spec. They get the entire model, the assembly, and the program notes because pulling out the right sheets takes time.
- Sharing runs through whatever tool is convenient. Personal email, free file-transfer sites, consumer cloud storage, a USB drive handed over at the loading dock.
- Nobody tracks where copies went. When the job closes, the drawings stay on the vendor's systems indefinitely, and the original company has no record of who received what.
None of this is unusual. The people sharing files are focused on schedules and quality, and the tools in front of them were never set up for regulated information.
What the rules require when you pass CUI down
The obligations come from a few places, and they stack.
DFARS 252.204-7012 is the clause that has required defense contractors to protect covered defense information (which includes CUI) using the security requirements in NIST SP 800-171 for years. Its subcontract paragraph requires the prime to include the clause, unchanged, in any subcontract where performance will involve covered defense information. It also puts a judgment call on the company doing the sharing: you are expected to decide whether the information a subcontractor needs still counts as covered defense information, and consult the contracting officer if it's unclear. If a subcontractor has a cyber incident, it reports to the Department within 72 hours of discovery and passes the incident report number up to you as soon as practicable.
DFARS 252.204-7020 adds a check before you award the work. A prime may not award a subcontract that involves covered defense information unless the subcontractor has a current NIST SP 800-171 assessment, completed within the last three years, posted in the Supplier Performance Risk System (SPRS).
CMMC flow-down under 32 CFR Part 170 requires the prime to pass down the CMMC level that matches the information the subcontractor will actually handle. A supplier that only touches federal contract information gets a Level 1 requirement. A supplier that processes, stores or transmits CUI needs Level 2. The Department of War suspended the Phase II rollout of CMMC on July 13, 2026, but Phase I self-assessment requirements stayed in place, and the 7012 and 7020 obligations above were never part of the pause.
The CUI program itself limits who can receive the information. Under the federal CUI rules administered by the National Archives CUI program, CUI can be shared when doing so furthers a lawful government purpose and isn't restricted by a limited dissemination control on the document. Some markings, such as export-control legends, narrow who can see a file even inside an approved subcontractor.
Cloud tools have their own requirement. The 7012 clause requires any cloud service used to store, process or transmit covered defense information to meet security requirements equivalent to the FedRAMP Moderate baseline. A December 2023 Department of Defense memo made clear that the contractor is responsible for confirming that equivalence. A consumer file-sharing account does not qualify, and neither does a standard business email plan by default.
What it costs when sharing goes wrong
The most visible cost is False Claims Act enforcement against contractors that claim to meet cybersecurity requirements and don't.
In March 2025, MORSECORP, a Massachusetts defense contractor, agreed to pay $4.6 million to resolve allegations that it had not implemented required NIST SP 800-171 controls, had not updated an inaccurate SPRS score, and used a third-party email provider that did not meet the FedRAMP Moderate equivalent requirement for covered defense information.
In December 2025, an Illinois precision machining supplier, Swiss Automation, agreed to pay $421,234 to resolve allegations that it failed to adequately protect technical drawings of parts it supplied to defense prime contractors. That is the situation in this post: a supplier holding drawings from customers further up the chain. Both settlements resolved allegations only, with no determination of liability, and both cases started with whistleblowers inside the companies.
The less visible costs are often larger for a company this size. A prime that finds its drawings on an unprotected vendor system can pull future work, and a supplier that can't answer a flow-down questionnaire confidently tends to lose bids without being told why.
How to share CUI with a subcontractor safely
The goal is a process the program and purchasing teams can follow without a security person in the room for every quote.
1. Share the minimum, on purpose
Before anything goes out, decide which pages, views or data the subcontractor actually needs. A coating shop may need the part outline and finish callouts but not the full assembly. A heat treater may need material and hardness specs, not the model. Sending less reduces both the risk and the number of systems that fall into scope.
Whether stripped-down information still counts as CUI is a decision for the prime and the contracting officer, not whoever is attaching files. Write down who makes the call.
2. Confirm the subcontractor can receive it
Before the first file moves, check three things:
- The subcontractor has a current SPRS score on file, as 7020 requires
- The subcontract includes the 7012 clause and the right CMMC level
- The person receiving the file is authorized, given any dissemination or export-control marking on it
Keep a simple register: subcontractor name, date of SPRS check, CMMC level flowed down, and contacts approved to receive CUI. It answers most questions a prime or auditor will ask.
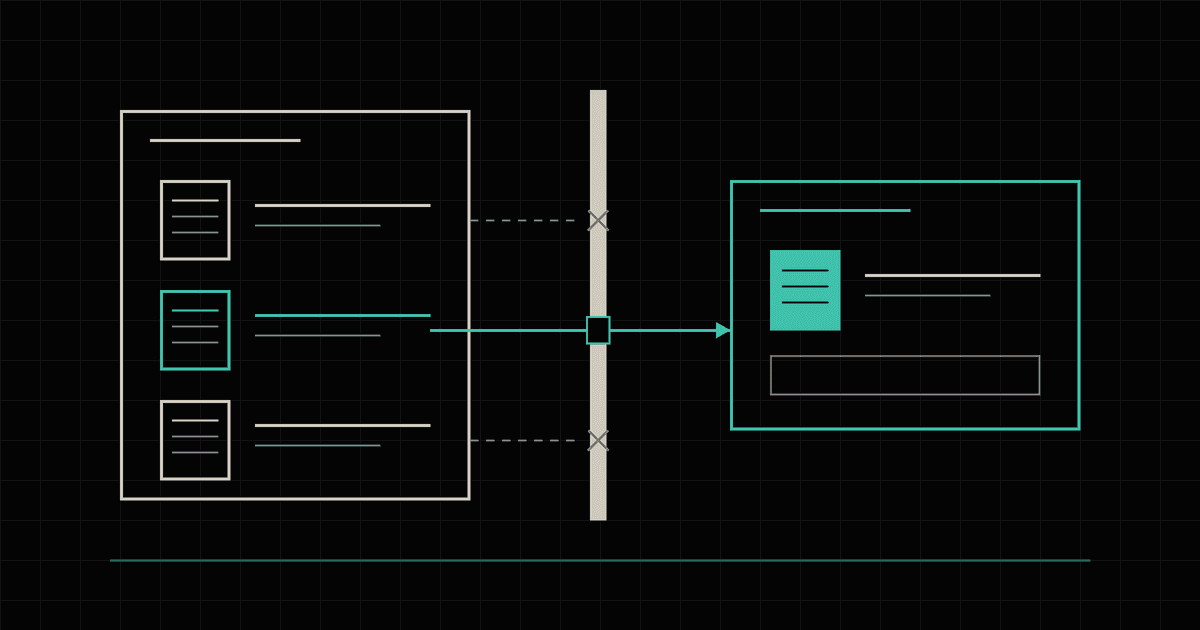
3. Use one approved channel and turn the others off
Pick one method for sending CUI outside the company, make it the easy option, and close the shortcuts.
| Sharing method | Fit for CUI | Main concern |
|---|---|---|
| Personal or free email | No | No control over storage or access |
| Consumer file-sharing link | No | Fails the FedRAMP Moderate requirement |
| Standard business email | Only with controls | Needs encryption and an approved service |
| Approved secure portal or enclave | Yes | Must be set up and kept current |
| USB drive or disc | Rarely | Hard to track, easy to lose |
NIST SP 800-171 expects CUI to be encrypted in transit with validated cryptography, removable media to be controlled, and the flow of CUI to be limited to approved paths. In practice that means a secure file-exchange portal or a CUI enclave that meets the cloud requirement, with email used only to send a link and never the files themselves. Email security rules can then flag or block outbound messages carrying CUI-marked attachments to outside domains.
4. Control access and keep a record
Every external user who receives CUI should log in with a named account and multi-factor sign-in, not a shared link anyone can forward. Access should expire when the job closes, and the portal's download log becomes your record of who received what.
5. Close the loop when the job ends
At closeout, ask the subcontractor to confirm in writing that CUI has been returned or destroyed, unless the contract requires them to keep it. Remove their portal access the same day. Note the closeout in the register.
6. Agree on incident reporting before you need it
Many primes add notice windows on top of the 7012 reporting rules. Make sure your subcontractors know who to call at your company, and that you know who to call at your prime.
How a managed security and vCISO approach handles it
This work splits into decisions and day-to-day controls.
The decisions are leadership work: which information counts as CUI for a job, which CMMC level to flow down, and which subcontractors are approved. A virtual CISO writes those rules down once, reviews subcontractor SPRS and CMMC status on a schedule, and answers the prime's flow-down questionnaires with evidence rather than guesses.
The controls are operational. Elevaire Managed Security runs the email rules that catch CUI-marked attachments heading outside, multi-factor sign-in and access hardening where CUI lives, device management that keeps CUI off unmanaged laptops and USB drives, and monitoring for unusual downloads. The quarterly security review checks that the subcontractor register and access lists still match reality. Elevaire works alongside the company's existing IT provider or internal team rather than replacing it.
For a formal assessment, an enclave buildout or a CMMC readiness program, Elevaire's compliance readiness work covers that as a quoted project.
Example engagement: a 90-person contract manufacturer receives drawing packages from two primes and sends portions of them to five local finishing and inspection vendors, mostly by email. Elevaire would map which vendors receive CUI and confirm each one's SPRS status, set up a single approved file-exchange portal with named accounts and multi-factor sign-in, add an email rule that holds CUI-marked attachments addressed to outside domains, and give purchasing a one-page procedure for each job.
Frequently Asked Questions
Can I email CUI to a subcontractor?
A plain attachment usually isn't enough. CUI has to be encrypted in transit, and any cloud email or storage service involved must meet the FedRAMP Moderate equivalent requirement in DFARS 252.204-7012. Most growing contractors find it simpler to use an approved secure portal and send only the notification by email.
Does the CMMC Phase II pause change what subcontractors need?
No, not for day-to-day sharing. The July 2026 suspension paused the move to required third-party Level 2 assessments, but Phase I self-assessments, the 7012 safeguarding and incident reporting clause, and the 7020 SPRS requirement all remain in force. Primes can also write stricter requirements into their subcontracts regardless of the federal timeline.
How much does it cost to set up secure CUI sharing?
Costs depend on how many systems hold CUI today and how many subcontractors you share with; the bigger driver is usually moving CUI out of everyday email and file shares. Elevaire Managed Security is offered at predictable monthly pricing with no hourly billing, and enclave or CMMC readiness work is quoted as a separate project. For context on the cost of getting it wrong, the two Justice Department settlements described above came to $421,234 and $4.6 million.
How does this work alongside our existing IT provider?
Elevaire handles the security side (email security, access controls, device management and monitoring) while your IT provider or internal staff keep running the systems they already manage. If your IT provider can reach systems that hold CUI, Elevaire coordinates with them so their access gets the same controls as everyone else's.
How do we get started?
Start by listing every subcontractor that has received CUI from you in the last year and how it was sent. That list usually shows where the gaps are. Then pick an approved sharing channel, check each subcontractor's SPRS status, and write down who decides what counts as CUI. Elevaire works with defense contractors and manufacturers on exactly this starting point.
About Elevaire Systems
Elevaire Systems is a managed security services provider for growing companies. We run your security tools and vendors, watch for threats and stop attacks for one predictable monthly price, with virtual CISO leadership and compliance readiness when you need more.
See Where Your Security Stands
Take the free 3-minute scorecard for your top security risks, or book a 30-minute Risk Snapshot to talk it through.